WP-SHELLSTORM: Exposed Server Reveals Mass WordPress Backdooring Operation
A cybercrime crew left its server open for 22 days, exposing a massive operation that backdoored thousands of WordPress sites using 27 CVEs, including CVE-2026-3844 in Breeze caching plugin.
Overview
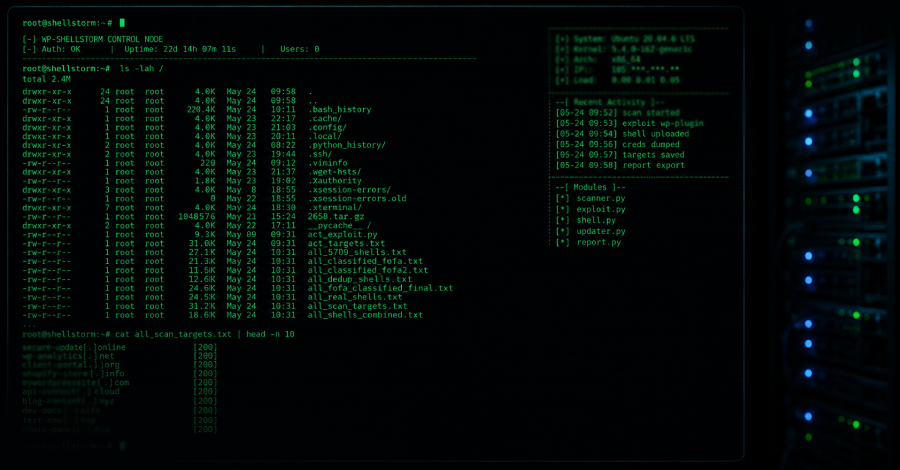
A cybercrime crew left one of its own servers wide open on the internet for three weeks, exposing the inner workings of a mass site-hacking operation tracked as WP-SHELLSTORM. The operation targeted over 1.4 million domains, primarily WordPress sites, using 27 known vulnerabilities to plant webshells for resale.
Discovery
On June 11, 2026, SOCRadar's Threat Intelligence Team spotted an open directory at 137.175.93[.]126 with no authentication. Inside was roughly 800MB across 434 files: webshells, exploit scripts, scan results, bash history, and C2 configuration. The exposure lasted 22 days due to a forgotten Python SimpleHTTPServer instance.
Key Vulnerabilities
- CVE-2026-3844 (Breeze caching plugin): Most exploited, backdoored over 17,000 sites.
- CVE-2026-48907 (Joomla JCE editor): Maximum severity, added to CISA's Known Exploited Vulnerabilities list.
- CVE-2026-3300 (Everest Forms Pro): Actively exploited.
- CVE-2021-29441 (Nacos): Used in a separate campaign against enterprise Java systems.
Impact
While 1.4 million domains were targeted, actual compromises were lower: Ctrl-Alt-Intel found 25,195 confirmed sites, while SOCRadar counted 5,700+ active webshells. The operation also included a quieter campaign in May 2026 that exfiltrated 613 configuration files from 11 systems across nine companies, stealing cloud credentials, database passwords, and Alipay RSA private keys.
Attribution
Both SOCRadar and Ctrl-Alt-Intel assess with medium-to-high confidence that the operator is Chinese or Chinese-speaking, based on Simplified Chinese in code, use of FOFA (requires Chinese phone number), and tooling like Godzilla and VShell. However, the crew is considered financially motivated rather than state-sponsored.
Recommendations
If you run WordPress or Joomla, patch immediately: Breeze (CVE-2026-3844, fixed in 2.4.5), Joomla JCE (CVE-2026-48907, fixed in 2.9.99.5). Also check ThemeREX Addons, Simple File List, Custom CSS JS PHP, BerqWP, Ninja Forms, WavePlayer, WPBookit, and WP File Manager. For Nacos, upgrade to 2.2.1+ and enable authentication. Hunt for webshells with patterns like .b* and down.php.