Hackers Use Fake Microsoft Entra Passkey Enrollment to Gain Microsoft 365 Access
A threat actor tracked as O-UNC-066 is using voice phishing and a custom phishing kit to trick Microsoft 365 users into enrolling an attacker-controlled passkey, enabling account takeover and data extortion.
Overview
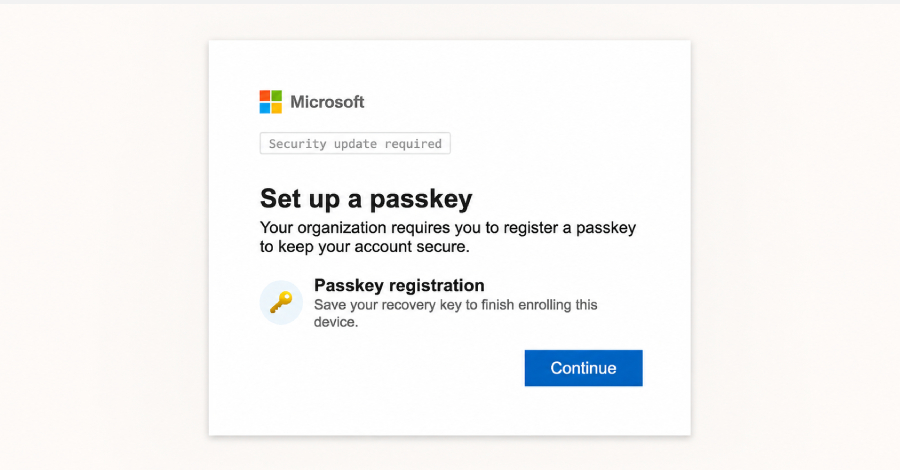
A threat actor has been targeting organizations across multiple sectors with voice-based fake security requests that prompt Microsoft 365 users to enroll a new Entra passkey, aiming to carry out data extortion attacks. The activity, tracked by Okta as O-UNC-066, uses a panel-controlled phishing kit that mimics the legitimate Microsoft passkey enrollment process.
Attack Vector
The threat actor registers domains containing the word 'passkey' and calls targeted users, persuading them to register a new passkey. Victims are directed to a phishing kit identical to Microsoft's passkey enrollment page. Instead of registering a passkey for the user, the attacker registers their own passkey against the victim's Microsoft account, granting unauthorized access.
Technical Details
The phishing kit is an operator-controlled PHP panel that guides victims through the enrollment process in real-time. The operator can adapt the user experience based on the victim's MFA requirements (TOTP, push notification with number matching, SMS OTP). The attack chain involves credential harvesting, MFA token capture, and a fake passkey registration ceremony that includes a recovery key (12-word seed phrase) as a distraction.
Attribution
Okta tracks the threat actor as O-UNC-066, while Palo Alto Networks Unit 42 tracks the cluster as CL-CRI-1147, describing it as affiliated with The Com, a decentralized cybercrime collective that includes Scattered Spider, ShinyHunters, and LAPSUS$. The actor has been operating a data leak site called Pink since April 2026.
Recommendations
Organizations should educate users about vishing attacks targeting passkey enrollment, enforce strict MFA policies, and monitor for unusual passkey registration activity. Administrators should review Microsoft Entra sign-in logs for unauthorized passkey additions.